How to Use Takumi
Using an AI agent to conduct security reviews
USECASE
Takumi Use Cases
Takumi is an AI agent that acts like a colleague who performs regular security reviews and other security operations
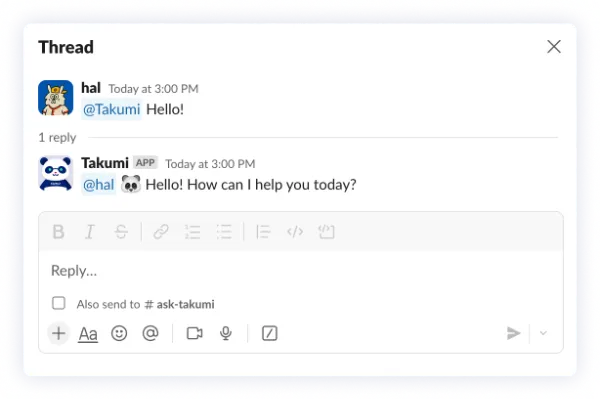
Communicate just like a colleague
Just as you would with a colleague, you use natural speech to interact with Takumi. On top of requesting security reviews, you can discuss design decisions or make inquiries about your source code. When you’re feeling a little stuck with your project, try chatting with Takumi and you may be surprised with what you can overcome with Takumi as a partner.
Scheduling Tasks
Takumi can operate 24/7 based on a schedule. You can schedule regularly occurring security reviews to stay up to date and one shot tasks for the after-hours.
Here is an example task that reviews all changes to the code from the previous day executed at midnight daily.
Check Prompt


Advanced usages
As you narrow down the scope of your request, the quality of Takumi’s output increases. This is easily said, but not always easy to do. One approach is to go ahead and make broad general request to Takumi to get started. Once you receive the report, you can start treating this like a conversation and ask follow up questions based on the report.
You can checkout the user guide for more detailed suggestions on advanced usages.
Check the User Guide
launch
HOW WE USE TAKUMI
Takumi at GMO Flatt Security
We introduce how Takumi is used internally
Tsubasa Umeuchi
GMO Flatt Security Software Engineer
Takumi gets increasingly more intelligent as you narrow down the space it needs to investigate, and specifying the relevant feature or the file path of the implementation are very effective ways to achieve this. Furthermore, if you can identify a specific concern or risk, or even better the type of vulnerability to investigate, it’ll drastically improve Takumi’s output quality.
That being said, I understand it’s often difficult to form a request with high specificity when starting work with a new application. In this case, I recommended you have Takumi put together an overview of the features and implementations of the application, and from there you’ll be able to use the results of the output to form more specified requests. To give an example, once Takumi discovers a vulnerability in some feature, you can request it to check other features for similar vulnerabilities, or ask where in the implementation the source of the vulnerability is at.
USECASES
Example Prompts

The Report by Takumi
This repository serves an online shopping service. This application implements authentication, item management, and payment, but contains several major vulnerabilities.
…
Application Overview
This application uses Prisma, Express.js, and Vue.js 3 to implement the online shopping experience.
Architecture
Frontend: Vue.js 3、TypeScript、Vuetify
Backend: Express.js、TypeScript、Prisma ORM
Database: PostgreSQL
Infrastructer: Docker/Docker Compose、Nginx、MinIO、Mailpit
…
Security Recommendations
Authentication
Add rate limting to log in and password reset functions
…
Access Control
Implement proper access control
…
Payment System
Implement transactions for inventory check and purchase operations
…
Error handling
Reconsider API schema to return only the necessary information
…
The Report by Takumi
Multiple vulnerabilities were found in path/to/directory. The most critical vulnerability is improper access control called IDOR. An attacker is able to access other users’ purchase data by specifying the relevant URL.
…
1. Impropre Access Control(IDOR)
Severity: High
Issue: In the xxx function, the user ID is obtained from the URL parameter, but there are no checks against the value for the authenticated user ID.
Scenario: An authenticated user can change the user ID parameter in the URL to access other users’ purchase data. For example, once logged in, user 1 can access /xxx?users=2&orders=123 to view user 2’s purchase data.
…
The Report by Takumi
Confirmed vulnerabilities related to CWE-287 (improper authentication). Several vulnerabilities were found related to account creation, log in, and password reset features. These vulnerabilities may lead to major security incidents.
…
1. Vulnerable password reset tokens
Severity: High
Issue: The token is only 5 characters, and an unsafe generation method is used.
Impact: Short predictable tokens are prone to brute force attacks and has the risk of a password being reset by an attacker.
2. Rate limit issue
Severity: High
Issue: There are no rate limits to the login and password reset features.
Reproduction:
Attempt multiple logins or password resets in a short time
Confirm the operations are successful without being stopped
Impact: An attacker is able to make an indefinite amount of attempts at log in or password reset.
…
Let's start by talking with Takumi.